CoordOps MSFVenom Payload Generator: Build and Review Commands in One Window
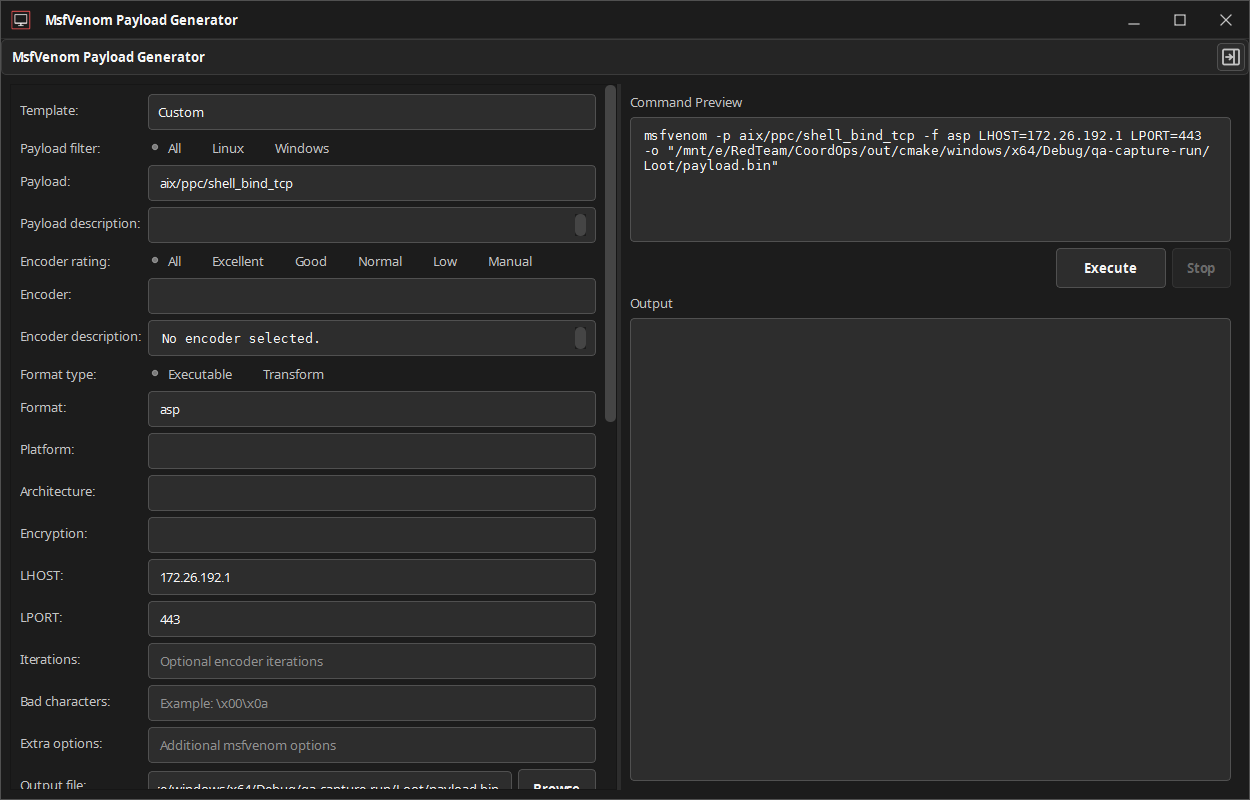
The CoordOps MSFVenom Payload Generator brings payload configuration into a focused desktop workspace for authorized penetration tests and red team operations. Instead of repeatedly assembling long command lines by hand, operators can select a payload, encoder, output format, platform, architecture, encryption method, connection settings, and advanced options from one interface.
The current CoordOps implementation includes 1,468 payload descriptions, 11 curated templates, 14 selectable encoders, 30 executable output formats, and 33 transform formats. Operators can filter payloads for Linux or Windows, filter encoders by quality rating, and configure options such as encoder iterations, excluded characters, encryption, NOP behavior, executable templates, output variables, and output files.
Every configuration change rebuilds the actual msfvenom command in the command-preview panel. This allows the operator to inspect exactly what CoordOps will execute before starting the process. Sensitive encryption material is redacted from the displayed and audited command, while execution output is streamed into the same session-oriented workflow used by other CoordOps tools.
The generator deliberately remains focused on payload creation. It does not automatically start a Metasploit handler or create a C2 listener. Operators remain in control of the receiving infrastructure and can pair the generated payload with the approved handler or command-and-control system appropriate for the engagement.